 OpsKnight
Access is an operational control.
Review roles, scoped authorization and session behavior. Provisioning and deprovisioning should be verified against the effective product permissions.
Read the operational guideSECURITY & IDENTITY
Connect identity, control access and inspect operational evidence on infrastructure you own.
WHAT IT SOLVES
Connect OIDC authentication and provision users and groups with SCIM. Enforce MFA at your identity provider; OpsKnight does not provide a native server-verified second factor.
Understand the capability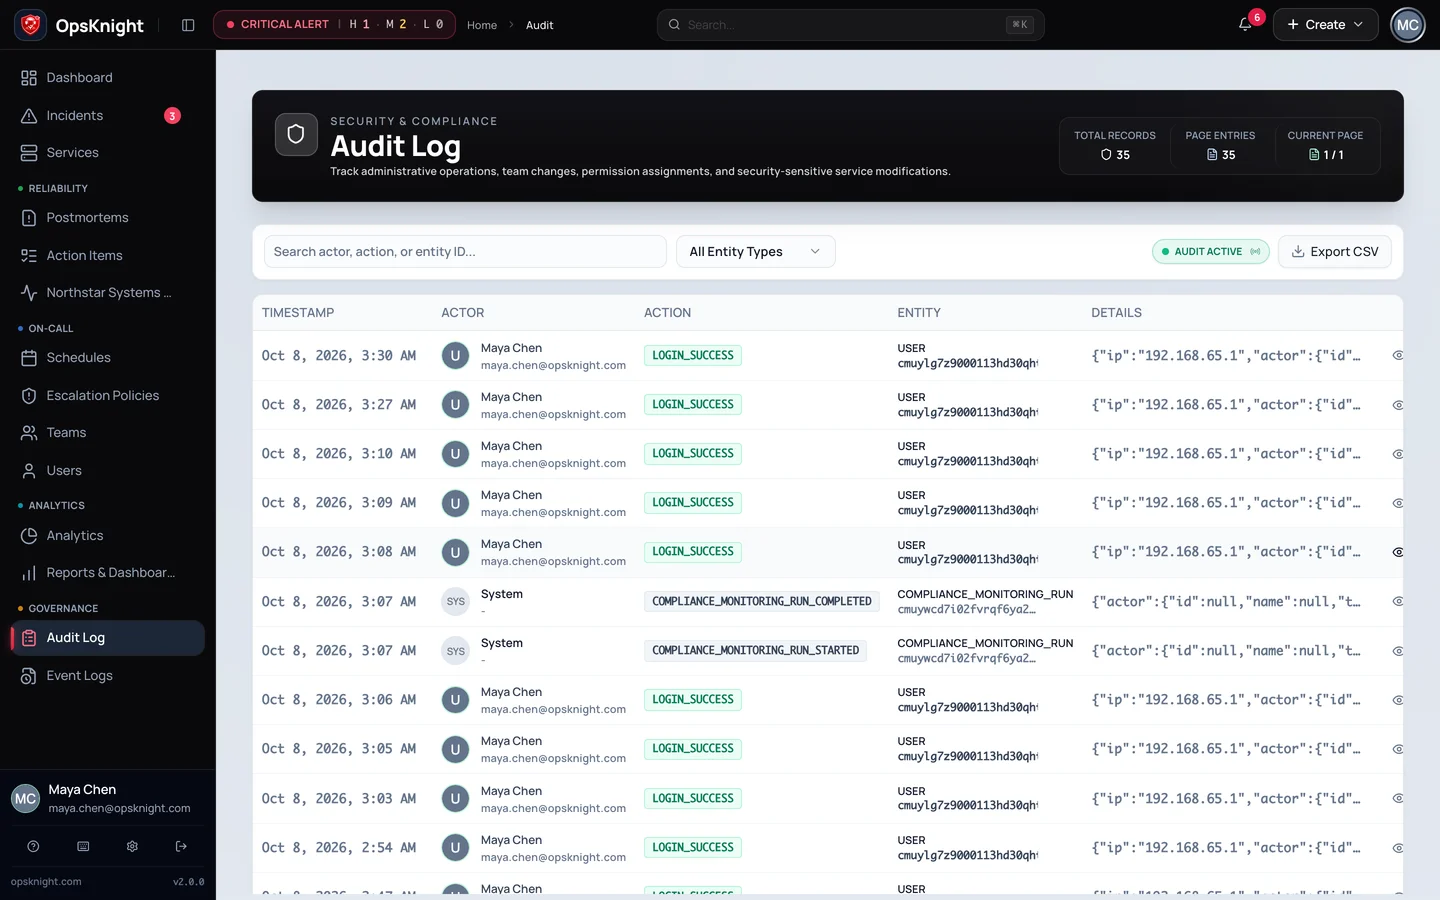
HOW IT WORKS
EXPLORE A WORKFLOW
Authentication, provisioning and authorization are separate controls. Validate the effective role after identity mapping.
OPERATIONAL DEPTH
The details below are the parts teams need when evaluating how the capability behaves during real response, failure, and handoff.
Review roles, scoped authorization and session behavior. Provisioning and deprovisioning should be verified against the effective product permissions.
Read the operational guideConfigure secrets, network access, HTTPS and recovery for your deployment. Preserve required encryption keys separately from database backups and follow the key-rotation guide.
Read the operational guideUse the security and procurement entry point for release policies, vulnerability handling, SBOM scope, supported versions and shared responsibility. These materials do not confer external certification.
Read the operational guideKNOW BEFORE PRODUCTION
Use a test service and representative provider configuration before treating security & identity as production incident infrastructure.
Run OpsKnight on infrastructure you control.
v2.0.0 · AGPL-3.0-only · Self-hosted · 28 inbound integrations